
Floin Cyberattack: MiCA Crypto Platform From Liechtenstein Goes Offline
Liechtenstein-based crypto platform Floin reports a cyberattack and has taken its app and web platform offline. What is known about the MiCA-licensed company, why deposit insurance does not apply and which alternatives investors have.




Which topics should we dive deeper into?
Select what genuinely interests you. Your picks feed directly into our editorial planning.
Crypto news that's actually worth your time.
Weekly. 60 seconds. Carefully curated by our editors: no hype, no promo flood, no spam.
Floin, a crypto platform based in Vaduz with a MiCA licence from Liechtenstein's Financial Market Authority FMA, says it has been the target of a cyberattack. On Saturday, 31 October 2026, Floin took all of its services offline: the app and the web platform are unavailable until further notice. In an email to customers sent at 10:54 UTC, the company warns users not to send anything to Floin wallet addresses, even if deposits are still technically possible. Floin has not said whether any customer funds were lost.
Key facts
- Incident: cyberattack according to Floin, customer email on 31 October 2026 at 10:54 UTC, app and web platform offline since.
- Warning: no deposits and no crypto assets to Floin wallet addresses, including from external wallets or other exchanges.
- Damage: by Saturday afternoon Floin had named neither an amount nor the affected coins.
- Supervision: MiCA authorisation from the FMA Liechtenstein since 10 June 2026, valid in all 30 countries of the European Economic Area.
- Deposit insurance: the €100,000 statutory deposit guarantee does not cover crypto assets; MiCA requires segregated custody and liability up to market value instead.
- Hack wave: the second incident at a centralised platform within 48 hours, after the Binance hack of 29 October with about $6.3 billion in losses according to Binance.
Floin cyberattack: what the platform tells its customers
The notice is short and leaves the key questions open. Floin writes that the platform was the target of a cyberattack, that all platform services have been taken offline and that access to the app and web platform is therefore unavailable until further notice. The investigation is ongoing and has the highest priority. The status page has listed the incident as “Investigating” since 10:30 UTC, and a banner on the homepage of floin.com shows the same notice. CryptoTicker has seen the email.
Three sentences matter for customers. First: no deposits into Floin wallets, not even from external wallets or other platforms, explicitly “even if deposits are still technically possible”. Second: Floin is currently not answering individual enquiries, including emails. Third: updates will only be published on its own website, and customers should check it daily.
It remains open when the attack began, which systems are affected, whether coins or customer data were taken and when withdrawals will work again. Anyone who still sends coins to a Floin address currently has no one to contact who could match them to an account.
Who is behind Floin: a MiCA crypto platform from Vaduz
The platform is operated by Floin AG, Am Schrägen Weg 2, 9490 Vaduz, founded on 29 January 2021 as The Finest Token AG and entered in the Liechtenstein commercial register under FL-0002.652.200-0. According to the imprint, the founder and CEO is Marc Weber. Under the share prospectus of 30 June 2026, he holds 90.01% of the capital; the remaining 9.99% belong to a Slovenian company in which he holds half. According to the commercial register extract, the chairman of the board is the lawyer Thomas Stern. Floin became known in 2023 for selling its own token, listed on floin.com today under the ticker FLTK: a private sale ran until mid-July 2023, and on 20 July 2023 Floin announced the start of the public sale. In January 2024, the security firm Halborn published a case study on Floin: auditing the smart contract and the platform, it found 34 vulnerabilities, all of which Floin fixed according to Halborn.
How big Floin is can be seen in the 2024 annual accounts that the company publishes itself: revenue of CHF 3.28 million (2023: CHF 3.63 million), a net profit of CHF 201,193 and share capital of CHF 250,000. The accounts were reviewed by the auditor Grant Thornton in Schaan.
At the same time, Floin is raising equity from its community. On its offering page, the company sells preferred shares of Floin AG as tokens called FLEQ, based on a prospectus approved by the FMA on 30 June 2026. The community round runs at CHF 1.44 per share, the minimum subscription is CHF 5,000, followed by a twelve-month lock-up. Floin cites a valuation of about €45 million; on Saturday the page showed 10,510 of 1,000,000 shares in this round as sold. In total, the offering covers up to CHF 7 million. MiCA custody protection does not apply to buyers of these shares: as shareholders, they carry the business risk.
In the MiCA register of the EU securities watchdog ESMA, Floin AG has been listed since 10 June 2026 with an authorisation from the FMA Liechtenstein for five services: custody of crypto assets for clients, exchange for funds, exchange for other crypto assets, placing and transfer. Through the EU passport, the licence applies across the European Economic Area, including Germany and Austria. Every customer email also carries the number 329177 as a registered virtual asset service provider (VASP) with the FMA.
What Floin told its customers in 2026 adds up to a dense timeline, compiled from the customer emails and the ESMA register:
| Date | Notice from Floin |
|---|---|
| 20 January 2026 | platform fees announced from 1 February 2026 |
| 26 February 2026 | self-custody wallets in the app from 9 March, in addition to the custodial Floin Custody wallets |
| 2 March 2026 | withdrawals of stablecoins such as USDC and EURC from custody wallets temporarily suspended, citing an opinion of the European Banking Authority on PSD2 and MiCA |
| 10 June 2026 | MiCA authorisation from the FMA Liechtenstein |
| 30 June 2026 | prospectus for the FLEQ preferred shares approved by the FMA |
| 15 September 2026 | brief interruption for scheduled maintenance |
| 12 October 2026 | Convert feature with fees, from 22 October also fees on sales and external transfers |
| 31 October 2026 | cyberattack, all services offline |
Floin and deposit insurance: what MiCA provides in an emergency
There is no deposit insurance for crypto assets as there is for a bank account, not even at a MiCA-licensed provider. The statutory deposit guarantee under EU Directive 2014/49/EU protects bank deposits up to €100,000 per customer and bank. Coins on a crypto platform are not bank deposits.
What the MiCA Regulation (EU) 2023/1114 requires instead:
- Segregated custody: crypto assets held in custody legally do not belong to the provider's estate, and the provider's creditors have no recourse to them in insolvency (Article 75(7)).
- Liability: if a provider loses crypto assets or the means of access to them through an incident attributable to it, it is liable to the client, capped at the market value at the time of the loss (Article 75(8)).
- Cash balances: client funds must be placed with a bank or a central bank by the end of the next business day, separate from the provider's own money (Article 70).
- Reporting duty: since 1 February 2025, the EU Digital Operational Resilience Act (DORA) also applies in Liechtenstein. Floin must report a major ICT incident to the FMA, with the initial notification usually within 24 hours of becoming aware of it (Article 19). Whether Floin has reported the attack is not known.
In practice, whether Floin customers get money back in case of a loss depends on what was taken and whether Floin covers it from its own funds or insurance. Floin's notice on Saturday does not mention a protection fund like Binance's SAFU.
Crypto hacks in quick succession: how attackers are getting through
Floin is the second incident at a centralised platform within 48 hours. On the evening of 29 October, about $6.3 billion left Binance according to the exchange, more than in any crypto hack before. We collect all major cases on our crypto hacks page.
The pattern of the big cases is the same: attackers do not break the cryptography, they break people and devices. At Binance, according to the exchange, the entry point was the compromised laptop of a DevOps engineer, through which the attackers reached a service container that releases withdrawals; who is believed to be behind it is covered in Binance hack: everything we know. The FBI attributed the Bybit hack of February 2025, about $1.5 billion, to North Korea. At Ledger, in December 2023, a phishing attack on a former employee was enough to publish a tampered version of a software library; customers lost about $600,000, BleepingComputer reported.
How the attackers got into Floin is unknown. One detail sets the case apart all the same: Binance named a loss figure on the day of the attack and shortly afterwards pledged to cover all customer losses. So far, Floin only points to its website.

Self-custody, exchange or broker: where your money is safer after the Floin hack
There is no place without risk, only different risks. On an exchange you carry the provider's risk, in your own wallet your own, and with a broker you usually buy a financial product on the price instead of coins.
| Own wallet | Crypto exchange with MiCA licence | Regulated broker | |
|---|---|---|---|
| Who holds the assets | you, via your recovery phrase | the exchange, separate from its own assets | the broker, securities separate from its own assets |
| What you own | real coins | a claim to real coins | for crypto usually only a CFD, a contract on the price |
| Typical attack | phishing, malware, tampered updates, extortion | attacks on staff, devices and withdrawal systems | account takeover via phishing |
| Protection in an emergency | none, what is gone is gone | liability up to market value under MiCA, plus a fund if the exchange has one | investor compensation for uninvested cash, at XTB in the UK via the FSCS up to £85,000 |
Self-custody makes you independent of Floin, Binance and every other platform, but solely responsible. Users of the software wallet Atomic Wallet lost more than $100 million in June 2023 according to Elliptic, which links the theft to North Korea's Lazarus Group. In January 2025, kidnappers in France abducted Ledger co-founder David Balland to extort a crypto ransom, as The Local reported. And how fast a single mistake can cost everything was shown on 30 October by an influencer who posted her private key instead of the contract address: Mika's memecoin drained in 81 seconds.
If you want to hold your own keys, you need a hardware wallet and a properly secured recovery phrase. We compare the devices in our hardware wallet comparison.
Regulated broker instead of crypto exchange: what XTB offers
An alternative that suggests itself after a week like this one: a brokerage account with shares, ETFs and gold, and crypto only as a small addition. One example is XTB. In the UK, XTB Limited is authorised and regulated by the Financial Conduct Authority; according to XTB, client funds are protected by the Financial Services Compensation Scheme up to £85,000 per person if the broker becomes insolvent. XTB offers shares and ETFs, while gold and cryptocurrencies are traded as CFDs.
For crypto this means: with a CFD you do not own any bitcoin, you cannot move it to a wallet or hold it yourself. You bet on the price. In return, there is no deposit address that can be hacked. XTB's mandatory warning, as of 31 October 2026: CFDs are complex instruments and come with a high risk of losing money rapidly due to leverage. 74% of retail investor accounts lose money when trading CFDs with this provider. You should consider whether you understand how CFDs work and whether you can afford to take the high risk of losing your money.
Open an account with XTB (partner link). How the broker performs in practice is covered in our XTB review, the alternatives in our crypto broker comparison.
 Crypto brokers compared: shares, ETFs and CFDs
What Floin customers should do now
- Send nothing to Floin addresses. Check recurring buys, standing orders and saved withdrawal addresses at other exchanges and wallets, and delete Floin addresses there.
- Beware of phishing. Hacks are followed by fake emails with supposed refund forms or support contacts. Floin says it will only inform customers via its website and is not answering individual enquiries. Never enter your recovery phrase or password anywhere.
- Secure your records. Save the statements, transaction receipts and screenshots you already have. You will need them for possible claims and for your tax return.
- Change passwords if you use your Floin password elsewhere, and check two-factor authentication there.
- Know the supervisor. Floin is supervised by the Financial Market Authority Liechtenstein, where you can file a complaint.
Anyone who has used a self-custody wallet in the Floin app since March holds the keys themselves, according to Floin's own description. The notice does not say whether these wallets are affected; the deposit warning applies to all Floin wallet addresses without distinction.
Our view: a MiCA licence is no shield against hacks
A MiCA licence proves that a provider must follow rules on custody, capital and liability and is supervised. It does not prove that it cannot be attacked. That applies to Floin as much as to any large exchange.
The real test for Floin starts now: how quickly the company says what happened, whether customer assets are affected and when withdrawals will resume. The longer these three answers are missing, the stronger the case for the split we recommended after the Binance hack: what you trade sits on a regulated exchange, what you hold long term on your own hardware wallet, and if you only want exposure to the price, a brokerage account can do that too. CryptoTicker asked Floin for a statement on the current situation on 31 October; we will add it here as soon as it arrives, along with any new information on the status page.
Disclosure: CryptoTicker's publisher holds a customer account with Floin that is not actively used; Floin's notice of 31 October arrived through it.
Frequently asked questions about the Floin cyberattack
Transparency note: This article was produced with the assistance of artificial intelligence and reviewed by our editorial team before publication. All figures and claims were checked against the primary sources linked in the text. The feature image was generated with AI.
Related articles
- Bitget Withdrawals Resume on September 28: What to Check on a Residual Balance Now
- Bitget discloses the flaw at its supplier and sets out the timetable for withdrawals
- Crypto Exchange Protection Funds Recalculated: What Really Covers Your Balance After the Bitget Hack
- Deutsche Bank to Custody Bitcoin and Ether: Why Retail Clients Are Missing and What to Check in Your Own Custody
- Crypto Exchange Shutting Down: What to Do Before the Deadline Passes
Which topics should we dive deeper into?
Select what genuinely interests you. Your picks feed directly into our editorial planning.
Crypto news that's actually worth your time.
Weekly. 60 seconds. Carefully curated by our editors: no hype, no promo flood, no spam.

August 30, 2026 10:38 PM
Crypto Cards: Where Your Card Balance Really Sits and What the August 28 Solana Exploit Reveals About It
An attack on a card balance contract on Solana took the loaded balance from 1,685 users while their wallets stayed untouched. The case shows why it matters whether your crypto card holds funds as e-money at a licensed institution or in a smart contract.
October 29, 2026 9:54 PM
Biggest Crypto Hack Ever? Binance Joins the List of Exchange Hacks
At about $2.8 billion the suspected Binance hack would be the largest theft a crypto exchange has ever suffered. The biggest crypto hacks at a glance, why exchanges are hit more often, what Tornado Cash has to do with it and what past cases meant for prices.
September 7, 2026 7:26 PM
Stolen Keys Beat Code Flaws: Why the Private Key Is the Way In for 2026 Crypto Hacks
Compromised private keys overtook smart contract code flaws as the most common attack route for the first time in 2026. What sits behind the shift, and how to check your own setup for its single point of failure.
September 29, 2026 7:12 PM
MEXC Refunds $340,000: The Attacker's API Key Survived the Account Freeze
During an account takeover at MEXC, an attacker created an API key with withdrawal rights that the exchange did not revoke when it restored the account. Twenty-seven minutes after the withdrawal freeze expired, roughly $340,000 was gone.
September 8, 2026 7:23 AM
Compensation After an Exchange Hack: What Twelve Crypto Providers Really Promise German Customers
After $322 million in losses in a single September week, the question is who replaces stolen coins. On September 8, 2026 we retrieved the security and legal pages of twelve providers and evaluated what is promised there.
August 21, 2026 4:27 PM
Wallet App Without BaFin Authorisation: When Holding Crypto-Assets Requires a Licence
On 19 August 2026 BaFin published two consumer notices on wallet offerings. Who controls the means of access decides whether an authorisation is needed.
October 30, 2026 12:40 PM
Binance SAFU fund: full reimbursement pledged for $6.3 billion
Binance puts the damage from the attack of October 29, 2026 at around $6.3 billion and intends to carry all losses, from the SAFU fund and from company funds. The fund holds 15,000 bitcoin, which at the current price comes to barely a fifth of the damage.

May 27, 2024 11:56 AM
Wave of Crypto Hacks and Exploits Hits Influencers and Memecoins: WATCH OUT!
A series of hacks on crypto influencers, celebrities, and a major memecoin exploit have raised serious security concerns within the cryptocurrency community. Here is what you need to watch out for!
October 29, 2026 12:28 AM

Bitget Wallet opens EUR accounts: incoming euros become USDT or USDC
Since October 27, 2026 Bitget Wallet gives its users their own account number in euros and US dollars, and the app converts incoming money automatically into USDT or USDC. What that means for SEPA transfers, the MiCA status of the two stablecoins and the holding period is set out here.
October 16, 2026 1:35 PM
Kraken parent Payward buys Saldo Bank: the first crypto firm with a bank of its own in the EU
Payward, the parent of Kraken, agreed on October 14 to buy the Lithuanian Saldo Bank and would be the first crypto firm with a bank of its own in the EU. What is established, what stays open until the planned completion in 2027 and what may change for the protection of your euros.

October 12, 2026 7:43 PM
Canton Coin Arrives in Ripple Custody: What Investors Need to Know
Ripple Custody has held Canton Coin and CIP-56 tokens since version 1.43. What the institutional custody solution means for you as a retail investor, and where you can trade CC in Europe at all.
October 5, 2026 1:29 AM
Chainalysis attributes $387 million from the Bitget hack to North Korea: what matters now for investors in Germany
The analytics firm Chainalysis attributes the theft of around $387 million at Bitget to actors with ties to the DPRK and puts the annual total above one billion dollars. What that means for custody, choice of exchange and record-keeping in Germany.
September 30, 2026 10:24 PM
$766 Million Lost to Crypto Hacks in One Month: What It Means for Your Custody
CertiK counts around $766.4 million in damage for September 2026, the highest monthly figure of the year. Two incidents carry more than 92 percent of it, and both hit a place where your balance could be sitting too.
September 23, 2026 10:11 AM
Kraken: 45 coins are on cancel only, 21 were announced – what to check when trading pairs are blocked
On September 23, 2026 we counted the public market directories of three trading venues. At Kraken, 82 of 1,450 trading pairs are listed as cancel only, a state in which an order can only be cancelled and no longer executed. The 45 underlying assets affected include just 21 that appear in the delisting notice we reported on September 3.
October 2, 2026 4:32 AM
NEAR Intents halts withdrawals after a $3.8 million exploit: here are the reasons
NEAR Intents confirms an exploit of more than $3.8 million and holds deposits and withdrawals on eleven networks. Reimbursement is promised, a date for it is not.
August 20, 2026 4:20 AM
Crypto Exchange Delisting: What Happens to Your Tokens When Trading and Withdrawals Close
A delisting runs in four stages, and only one of them is genuinely dangerous: the end of the withdrawal deadline. Using two live OKX dates as the example, we show what happens at each stage and how to tell whether it affects you.
July 2, 2026 8:59 PM
Binance Is Out of the EU: How to Move to a MiCA-Regulated Exchange
Binance has left the EU market. Which exchanges hold a MiCA licence, how to verify an authorisation is real, and how to move your holdings across step by step.
October 27, 2026 12:48 PM
Bloom trading bot: 9,408 SOL drained, what to watch now
The Telegram trading bot Bloom reports an outflow of 9,408 SOL from 49 addresses and points to a flaw in a third-party module. The provider promises reimbursement in full; the decisive question about the key remains open.
October 11, 2026 1:24 AM
Three Mistakes When Setting Up Trust Wallet: The Twelve Words Never Belong on the Phone
Trust Wallet is set up in five minutes, yet three mistakes in those minutes regularly cost the entire balance. This guide covers the six steps, the real cost of a swap, and what applies in Germany on the holding period and supervision.
October 6, 2026 10:32 AM
FinCEN drops the reporting duty for withdrawals to private wallets: what matters now for European investors
The US anti-money-laundering agency FinCEN withdrew two proposals on October 5, 2026 covering the reporting duty for self-custodied wallets and for mixers. In the EU the development runs in exactly the opposite direction: proof of ownership from 1,000 euros today, a ban on anonymous accounts from July 2027.
September 27, 2026 4:32 AM
Hester Peirce Leaves the SEC: What Now Applies to Your Custody in Germany
The most crypto-friendly voice at the US securities regulator goes on October 2, 2026, and the commission shrinks to two members. For investors in Germany it is still the European rulebook that decides, and there a deadline falls in July 2027.
September 4, 2026 10:26 PM
Pocket Bitcoin Data Breach: When Name, Home Address and Bitcoin Address Circulate Together
The Swiss Bitcoin service Pocket Bitcoin closed its investigation on September 3, 2026: 5,411 people affected, and for 291 of them the Bitcoin addresses they used along with copies of identity documents. Why this one data pairing has lasting effect, and what you should check with your own provider.
September 3, 2026 4:41 AM
Kraken Delists 21 Tokens: Trading End on September 11 Has Passed, Withdrawals Run Until December 10
As of September 27, 2026: Kraken had set the end of trading and deposits for 21 cryptocurrencies for September 11, 2026 at 14:00 UTC, and that date has passed. According to the exchange, withdrawals remain possible until December 10, 2026 at 15:00 UTC. Our September 3 survey showed that none of these tokens could be deposited at Bitvavo, Coinbase or Bitstamp.
August 6, 2026 3:05 PM
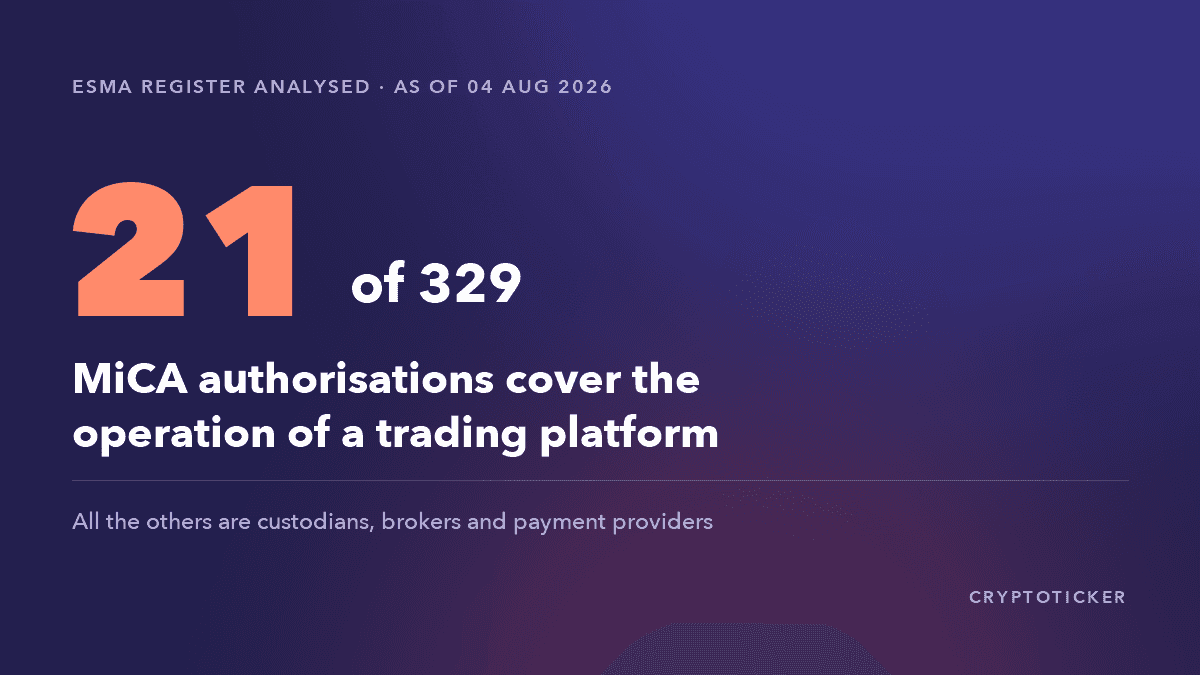
MiCA Register 2026: Only 21 of 329 Licences Are Real Exchanges
ESMA publishes the register of MiCA-authorised providers as an open file. We worked through all of it — and the result is not what the phrase “licensed crypto exchange” suggests.
August 11, 2026 9:18 AM
Your Crypto Exchange Is Telling You to Withdraw: How to Spot Phishing After the MiCA Deadline
Unauthorised crypto providers now have to tell their EU customers to withdraw, which leaves fraudsters an easy run with faked requests. Here is how to check in two minutes whether the message is genuine.

June 30, 2026 11:20 PM
How to Switch from Binance to a MiCA Regulated Crypto Exchange
Binance is winding down EU services after missing the MiCA deadline. Here's why it's happening and how to move your funds to a regulated platform safely.
September 10, 2026 1:21 AM

Crypto Exchanges Head to Head: Which Pairing Is Cheaper Where
Before opening an account, the question is rarely which exchange is best overall, but whether it should be this one or that one. This article sorts through the most searched head-to-heads, puts the cost per 1,000 euros side by side and explains the most expensive mix-up: one provider with two interfaces and a factor of seventeen between them.
More from CryptoTicker