
Ledger Hack? $86 Million Drained: What Is Behind the Tampered Wallets From Southeast Asia
Since Friday, Ledger users in Southeast Asia have been reporting empty wallets, and analysts count more than $86 million. Ledger has halted the reseller CryptoBilis. An implant inside the device reportedly reads the seed phrase. What is known, what CZ advises and what you should do now.




Which topics should we dive deeper into?
Select what genuinely interests you. Your picks feed directly into our editorial planning.
Crypto news that's actually worth your time.
Weekly. 60 seconds. Carefully curated by our editors: no hype, no promo flood, no spam.
Update 13 October 2026: Ledger has since confirmed that an implant inside the device read the recovery phrase from the screen during setup and sent it to the attackers over LTE. On 13 October, MediaMarkt Saturn also stopped selling Ledger devices in Germany, in stores and online, after a customer reported an implant; according to Ledger, no funds were lost in that case. More: Ledger confirms implant in hardware wallet.
First Coldcard, now Ledger. Two months after more than $116 million drained out of Coldcard Bitcoin wallets, the world's best-known hardware wallet is in the spotlight. Since Friday morning, 9 October 2026, users in Southeast Asia have been reporting empty wallets on X and Reddit. On-chain analysts now count more than $86 million that has flowed to a handful of collection addresses. Ledger has confirmed an investigation and halted one of its official distributors: CryptoBilis, a reseller that sells Ledger devices in Indonesia, Malaysia and the Philippines.
The most important point first: based on everything known as of Friday evening, Ledger itself was not hacked. The supply chain was. The trail leads to devices sold through a single middleman. If you bought your Ledger directly from the manufacturer, there is no indication so far that you are affected. For everyone else, there are clear steps, summarised further down.
Ledger Hack: What Happened on 9 October
The first major alert came from the pseudonymous blockchain investigator Specter at 12:24 UTC. He had followed up on reports from Ledger users about drained wallets and published ten collection addresses on Bitcoin, Ethereum and Tron that, in his view, received funds from hundreds of victim wallets. His total: more than $86 million. A quarter of an hour later he added that he had not yet been able to determine the exact number of affected wallets. A second analyst, tanuki42, puts the losses at more than $72 million and is asking victims to contact the volunteer emergency group SEAL 911. The analytics firm MistTrack spoke of almost $90 million in the afternoon.
The analytics platform Arkham, which now labels the collection addresses "Ledger Theft", shows what the pattern looks like. On Friday morning, the Tron address tagged TBkcU received ten USDT transfers in quick succession, each between $500,000 and $2.4 million. Around midday two more deposits of $740,000 and $508,000 arrived at two other addresses. These are not small investors losing a few hundred dollars. These are wallets in which people kept their savings.
At 13:32 UTC, Ledger responded through its support account. The company said it is investigating reports of losses among users in Southeast Asia who bought products from CryptoBilis. As a precaution it has asked the reseller to pause all sales and shipments of Ledger devices. Anyone who bought there in the past 90 days and has not set up the device yet should not do so. Anyone who already has should move their assets to a new Ledger device with a new seed phrase.
What the statement leaves out is telling: a number, a cause and the word hack. Ledger neither confirms the $86 million nor explains how the seeds ended up in someone else's hands. Neither the total nor the cause has been independently confirmed so far. The only established facts are the halt at the reseller and the advice to its customers.
| Time (UTC) | What happened |
|---|---|
| from approx. 06:00 | Ten USDT transfers of $0.5M to $2.4M arrive at the Tron collection address TBkcU |
| 12:24 | Specter publishes ten collection addresses and cites more than $86M |
| 13:32 | Ledger confirms its investigation and halts the reseller CryptoBilis |
| 14:01 | Binance founder Changpeng Zhao calls it a supply chain attack at one vendor |
| afternoon | MistTrack cites almost $90M, Tether freezes linked USDT addresses |
| from 15:37 | Mark Karpelès describes a spy implant inside the device that passes the genuine check |
Part of the loot may still be frozen. According to MistTrack, stablecoin issuer Tether has already frozen USDT on addresses linked to the thefts. How much is affected is unclear. There is no such lever for Bitcoin and Ether: once funds have left, only an exchange can still stop them when the thief tries to cash out.
Update 16:30 UTC: The attacker has started laundering. According to Onchain Lens, 430.2 ETH, roughly $1.07 million, went into the Tornado Cash mixer across four wallets. Following Tether's freezes, the attacker is also swapping USDT into USDD, a Tron stablecoin that Tether cannot freeze. The longer this goes on, the smaller the share of the loot that can still be recovered.
 Find the right hardware wallet for your coins
How the Wallets Were Emptied: The Implant Inside the Device
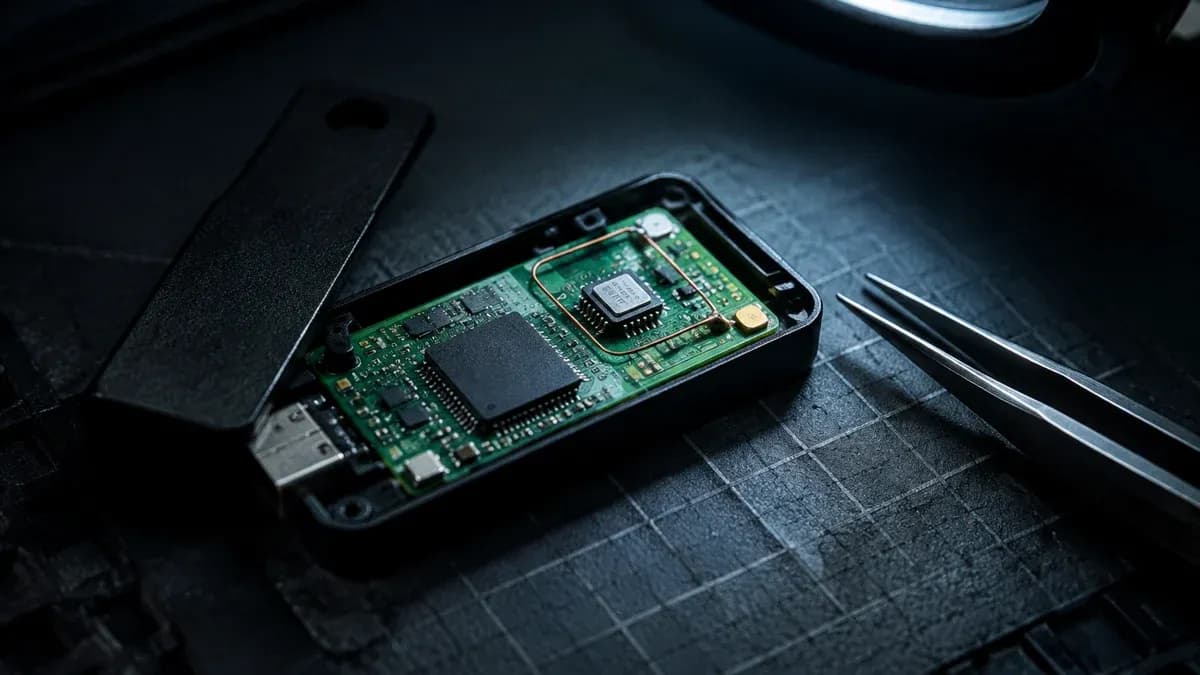
The most concrete explanation so far comes from a man the crypto world knows from a very different context: Mark Karpelès, former head of the Mt. Gox exchange that collapsed in 2014. Karpelès has been examining tampered Ledger devices for weeks and had already shown photos of a modified Nano X in September. On Friday afternoon he put the new cases into context in a series of posts. His description: an extra chip sits inside the casing, reads what appears on the screen, records the seed phrase at the moment the device displays it for you to write down, and transmits it.
The dangerous part: according to Karpelès, such a device passes Ledger's genuine check. The actual secure element is real, it generates the seed correctly and signs properly. It is simply being watched. In his words, the only way to detect the implant is to open the device. Earlier versions gave themselves away with sloppy shrink wrap, the new one is far better made and hidden under the display. The most obvious tell is an antenna cable that looks clearly out of place inside. Ledger has a support page with photos of what the inside of a genuine device should look like, and Karpelès is asking CryptoBilis buyers to open their device and share pictures.
One detail from his posts should alarm anyone who orders hardware wallets online. His own test device had struck him as suspicious because it was listed on Amazon at half price and shipped from Malaysia instead of Japan, where he had ordered it. The origin was the warning sign before he ever opened the case.
Whether every case goes back to an implant is still open. The developer 0xQuit considers it just as possible that some victims fell for phishing, and calls it irresponsible to speak of a Ledger hack. At the same time, security researcher CyberScrilla is warning about a fake Ledger site that ranked at the top of Google Search and, by his account, had more than a million visits in 30 days. It asks for the seed phrase. There is no confirmed link to the $86 million, but the rule applies regardless: a seed phrase never belongs in a website or an app.
It is just as important to understand what this attack is not. It is not a firmware bug like at Coldcard, where a predictable random number generator gave away the seeds. It is not an attack on Ledger's servers and not remote access to every device worldwide. It is an attack on the path a device takes from the factory to you. That is also where the reseller comes in. Whether CryptoBilis itself introduced tampered devices, whether there was an offender in its warehouse, or whether the reseller was itself supplied with counterfeit goods is not known. So far Ledger has only halted sales and has made no accusation.
Ledger in Second Place: Hardware Wallet Incidents of 2026 Compared
How big is this case by comparison? In the afternoon, the on-chain service Chain INK compiled all hardware wallet incidents of the year in one list. Only two of them have demonstrably cost customers money so far: Coldcard and now CryptoBilis. Coldcard is still ahead in total losses at $111 million, and other counts put it as high as $130 million. Less than a day in, the Ledger case already ranks second at $87 million, and the count is still running.
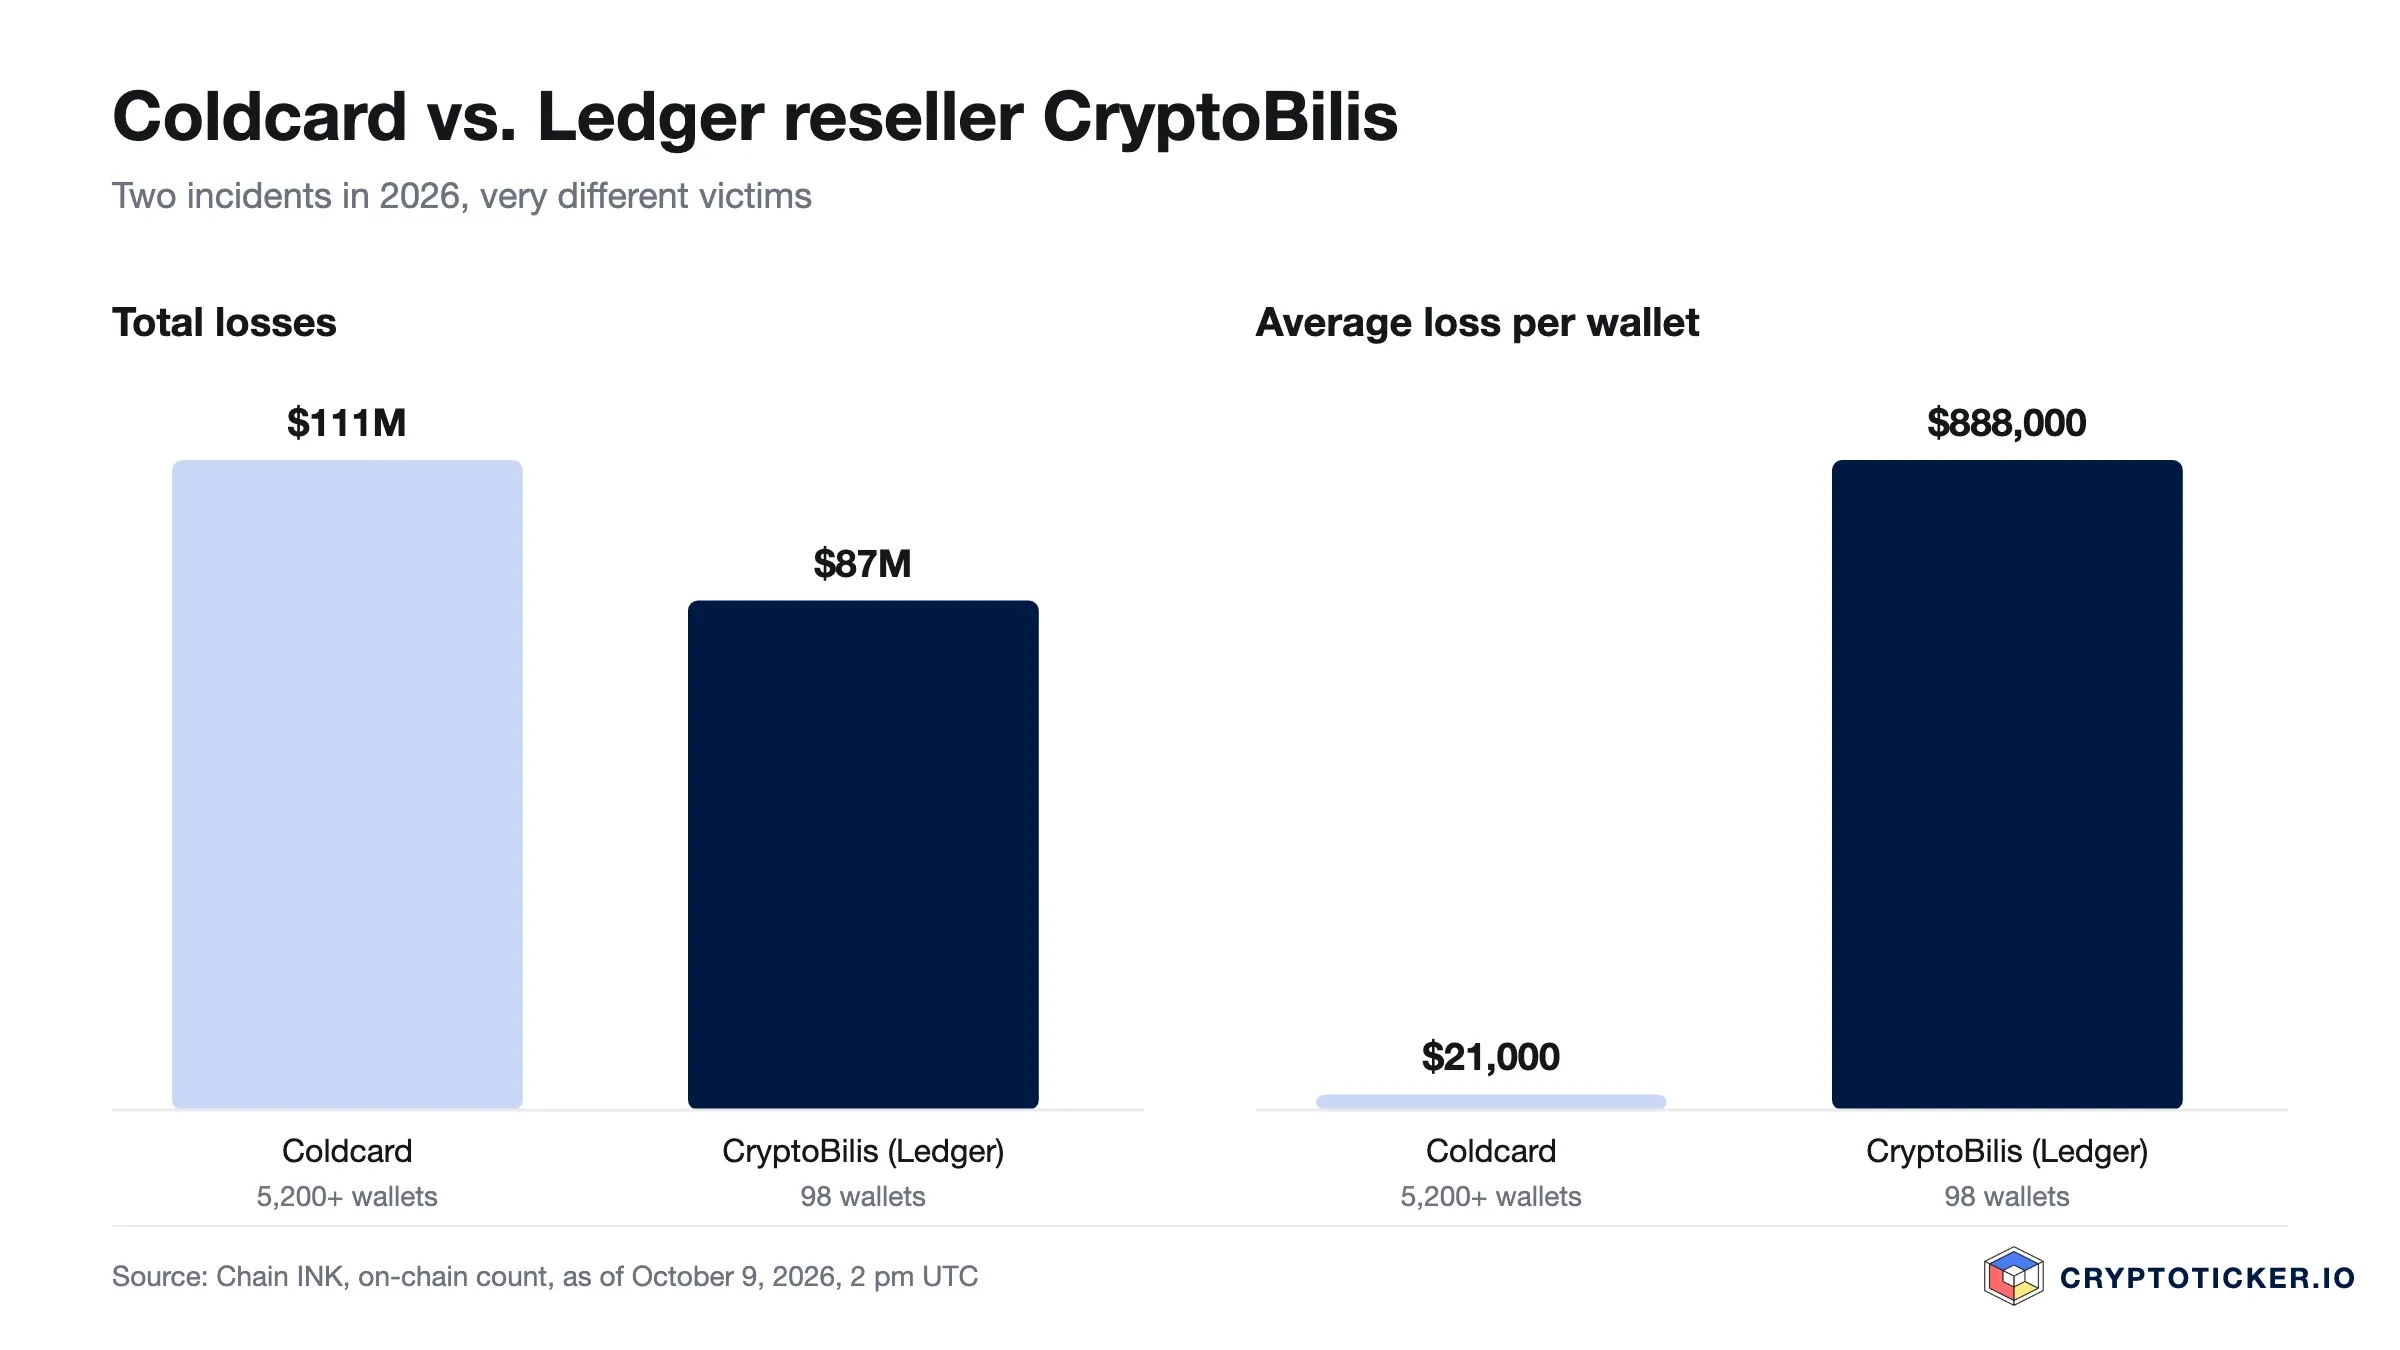
The real difference lies in the second number. At Coldcard, the damage was spread across more than 5,200 wallets, around $21,000 per wallet on average. At CryptoBilis, Chain INK counts 98 wallets, which would mean almost $890,000 on average. Even if Specter's estimate of several hundred victim wallets is confirmed, the average remains many times higher than in the Coldcard case. That fits the pattern of an implant: the attacker knows every seed created on the tampered devices and strikes selectively where it pays off.
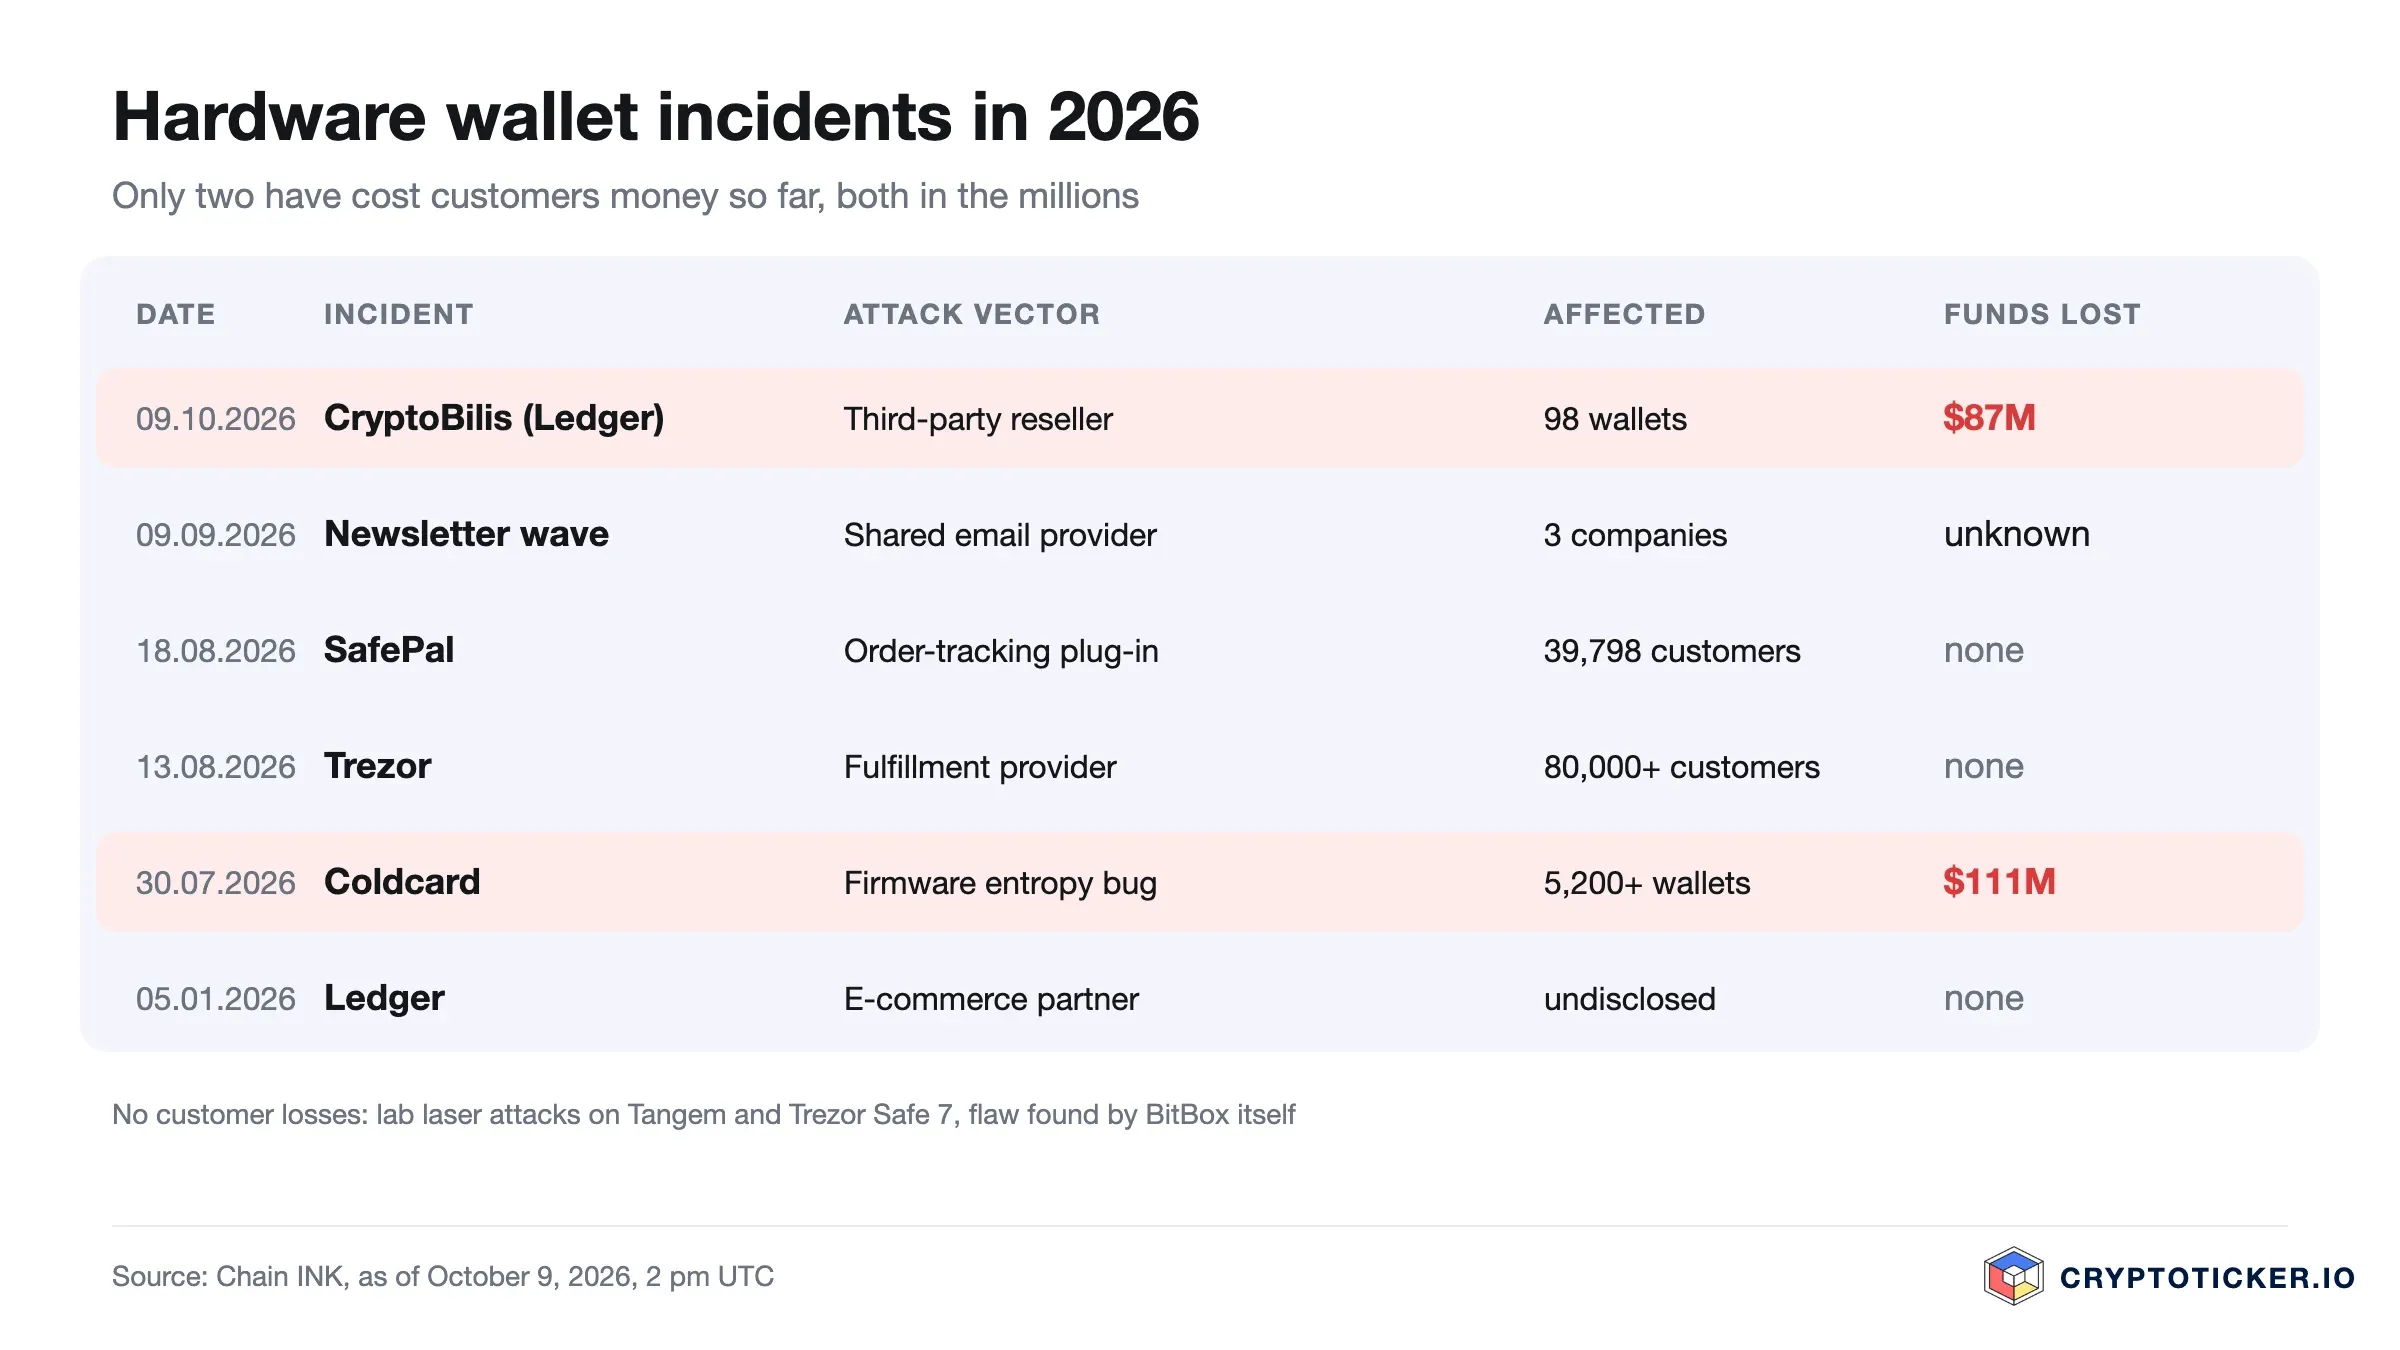
Three more entries on the list are left out of the table because they did not hit any customers: two lab attacks using a laser on the chip, at Tangem and on the Trezor Safe 7, and a BitBox02 flaw the manufacturer found and fixed in its own audit. The common thread of the table is a different one. Five of the six incidents did not come through the device but through third parties: a reseller, a fulfilment provider, a shop plug-in, an email provider, a sales partner. On top of that come fake letters with QR codes that have been sent to wallet owners for months. Chain INK sums it up: nobody had to crack a seed phrase this year.
Ledger and the Supply Chain: Not a New Problem
The attack route is not new. In December 2020, unknown actors published the names, postal addresses and phone numbers of around 270,000 Ledger customers from a data breach in the summer of 2020. In spring 2021, customers then received supposed replacement devices by post with a letter from "Ledger". Anyone who opened one found an extra memory chip soldered on. In December 2023 it was the software's turn: a tampered update of the Ledger Connect Kit library redirected wallet connections on numerous DeFi sites for several hours. Tether froze part of the loot back then as well. And in May 2023, the Ledger Recover service, which lets users store encrypted parts of their seed with third parties, cost the company a great deal of trust within its own community.
Each of these cases had a different cause. What they have in common is that the core never failed, meaning the secure element, but everything around it did: customer data, software suppliers, distribution channels. For Ledger, that is more uncomfortable than a firmware bug. A bug in the code can be fixed with an update. A reseller network in which an official partner can ship tampered devices cannot be repaired with an update. How Ledger supervises its authorised resellers is a question the company will have to answer in the coming days.
What CZ Advises, and Why the Tip Does Not Help Here
The most prominent comment of the day came from Binance founder Changpeng Zhao, better known as CZ. At 14:01 UTC he wrote that, based on the information so far, it appears to be a supply chain attack at a single vendor, and that a small number of people probably bought fake or tampered Ledgers. In a second post he offered a security tip: leave a new hardware wallet for a couple of weeks before moving any meaningful amount to it, and follow the news during that time.
That sounds sensible but does nothing against this particular attack. An implant that captures the seed phrase during setup knows your wallet from day one. The attacker has no reason to sweep a $50 test transfer and give himself away. He waits until the wallet is worth it. If you test small amounts for two weeks and then move your savings over, you have gained nothing. The only protection is a device that verifiably came straight from the manufacturer.
Then there is the question of who is handing out advice on safe custody. In November 2023, Zhao pleaded guilty in the United States to failing to maintain an effective anti-money-laundering programme at Binance, a violation of the Bank Secrecy Act. He stepped down as CEO of the exchange and paid a $50 million fine, while Binance itself settled with US authorities for $4.3 billion. In 2024 he served four months in prison, and in October 2025 US President Donald Trump pardoned him. Zhao was not charged with fraud. Still, the founder of the largest centralised exchange, a business built on third-party custody, giving self-custody advice is a bold move.
 Get the key crypto news in your inbox
Bought a Ledger? Here Is What You Should Do Now
Whether you need to act depends almost entirely on where your device came from. Go through the following points in order.
Bought from CryptoBilis in the past 90 days, not yet set up: Do not switch it on, do not set it up. Ledger explicitly advises against it. Keep the device, packaging and receipt, and contact Ledger through its official support page.
Bought from CryptoBilis and already set up: Treat your seed phrase as known. Buy a new device directly from the manufacturer, create a new seed on it and move all your coins, and do it now, not after the investigation. Adding a passphrase on the old device is not enough if the implant reads whatever appears on the screen.
Bought on a marketplace, second-hand or at a suspicious discount: The same risk applies, even without CryptoBilis. If you bought through Amazon, eBay, Shopee, Lazada or classified ads, you do not know which route the device took. The same advice applies as above, at least for larger amounts.
Bought directly from Ledger: As things stand, there is no indication that devices from the Ledger shop are affected. Still, check that your device generated a new seed on first start and that no pre-printed recovery card with words was included in the box. A seed you did not create on the device yourself is never yours alone.
Already lost funds: Save the transaction hashes and the address the funds went to, contact SEAL 911 and file a police report. If USDT was lost, also notify Tether through its support, because Tether can freeze balances on attacker addresses as long as they remain there. The faster you act, the better your chances.
If you hold larger sums, consider a multisig setup, meaning a wallet that needs two or three devices from different manufacturers to sign. A single tampered device is then no longer enough for a theft. Which devices are suitable and where to get them directly from the manufacturer is shown in our hardware wallet comparison. After the Coldcard case we also explained in detail which hardware wallet you can still buy with a clear conscience.
Why We Do Not Ship Hardware Wallets
This case shows why the distribution route matters as much as the device. CryptoTicker does not sell or ship hardware wallets. Our comparisons and product pages describe the devices, and the purchase happens with the provider. For Ledger, OneKey and Tangem, the buy button leads directly to the manufacturer's official shop, so the device goes from the manufacturer to you without any stop in between. After today, exactly this route, with no third-party warehouse in between, is the most important property when buying a hardware wallet. A discount of a few dollars at a middleman is no compensation for the risk that someone opened the case before you.
What You Should Take Away From the Ledger Case
Two of the best-known hardware wallets in two months, both times damage in the region of $100 million, and both times the failure was not where the marketing promises security. At Coldcard it was randomness, at Ledger, as things stand, it is the route from the factory to the customer. None of this is an argument against self-custody. On an exchange your funds would face entirely different risks. What follows is that a hardware wallet is only as secure as its origin and the moment the seed is created.
Three rules remain. Only buy directly from the manufacturer. Always create the seed yourself and never accept one that was already in the box. And spread large holdings so that a single device cannot give everything away. Ledger has promised updates on its investigation. We will update this article as soon as the cause and the size of the losses are confirmed.
Frequently Asked Questions About the Ledger CryptoBilis Case
Transparency note: This article was produced with the assistance of artificial intelligence and reviewed by our editorial team before publication. All figures and claims were checked against the primary sources linked in the text. The feature image was generated with AI.
Related articles
- Ledger Confirms Implant in a Hardware Wallet as Reports Reach Europe: What Is Behind It
- MediaMarkt and Saturn halt Ledger sales after a customer reports an implant
- Trezor cuts its authorized dealers: the authorizations end on January 1, 2027
- Breaking: Trust Wallet Chrome Extension Hack Drains $7M, Full Reimbursements Promised
- $13.84 million in 48 hours: Arkham says the drainer is “still moving funds”
Which topics should we dive deeper into?
Select what genuinely interests you. Your picks feed directly into our editorial planning.
Crypto news that's actually worth your time.
Weekly. 60 seconds. Carefully curated by our editors: no hype, no promo flood, no spam.

August 5, 2026 10:33 PM
$130 Million Gone Because the Randomness Was Predictable: Which Hardware Wallet You Can Still Buy
The Coldcard flaw proved the most respected wallet is not the safest. Which vendor has which track record – and why now is the wrong moment to pause your savings plan.

July 31, 2026 3:54 PM
594 BTC Gone in 25 Minutes: The Coldcard Flaw That Made Seed Phrases Guessable
A firmware bug from March 2021 let an attacker drain $38 million from around 500 Bitcoin wallets. Here is what broke, who is exposed and what to do now.
October 19, 2026 1:14 AM

Qubic halts its mainnet after 1,404 wallets are drained: the seed was the weak point
An attacker drained 1,404 Qubic wallets on the night of October 18, roughly $1.3 million. The protocol was not to blame: seed generation in the browser supplied too little randomness.
October 29, 2026 9:38 PM
Binance Hack: Around $2.8 Billion Drained From a Hot Wallet
On Thursday evening, roughly $2.8 billion left the Binance wallet “Binance 14” within minutes. The attacker had tied the wallet to their own contract via EIP-7702. Tether and Circle have frozen about $2.4 billion, and Binance says it is investigating.
October 16, 2026 4:41 PM
Fake Ledger firmware updates: SlowMist reports phishing pages with a replica Genuine Check
A phishing campaign reproduces the sequence of an official Ledger update and asks, at the end, for the 24 recovery words. SlowMist reported it on October 16; Ledger had set out its reading of the underlying implant case a day earlier.
September 29, 2026 10:14 AM
Bitget discloses the flaw at its supplier and sets out the timetable for withdrawals
Bitget has disclosed how the attackers reached its withdrawal systems on September 24: through a previously unknown flaw in a security product it had bought in. The second stage of the withdrawal schedule opens today at 08:00 UTC, and for the balance you keep on any exchange the case changes the arithmetic.
September 10, 2026 9:13 AM

Trezor Hack Scare: That STM32 Entropy Email Is a Phishing Attack
Trezor users received a fake STM32 entropy warning sent from a real Trezor address. Here is what happened and what to do if you clicked.
August 22, 2026 4:13 AM
SafePal Data Breach: 39,798 Customers Exposed With Names, Addresses and Phone Numbers
SafePal confirmed a data breach on August 16, 2026: the names, delivery addresses, phone numbers and order details of 39,798 customers were exposed. Seed phrases and private keys were not affected, but the phishing risk is substantial.
August 13, 2026 4:59 PM

Trezor Data Breach: First 13,689 Customers, Then Roughly 67,000 More Exposed
A breach at Trezor shipping partner ShipMonk exposed names, phone numbers and home addresses of 13,689 customers in August; in September Trezor reported roughly 67,000 more in the US. Devices are safe, phishing risk is not.
August 4, 2026 1:21 PM
Coldcard Losses Near $114 Million as a Fourth Sweep Hits: Why Is Bitcoin Rising Anyway?
A fourth wave of Coldcard sweeps took another 449 BTC on Monday, yet Bitcoin climbed back toward $64,000. Here is what changed and who is still exposed.
September 27, 2021 2:58 PM
What Is Bitcoin? Bitcoin Explained: Halving, Supply and How to Buy
Analysis: What Bitcoin is and how it works, explained simply with current figures on supply, halving and hash rate, plus how to buy, store and tax bitcoin and our view on the risks.
October 28, 2026 12:51 PM
Keystone destroys 18,835 hardware wallets, shipping on hold
The break-in on Keystone's website leaked the key owners use to verify their hardware wallet. Because it sits in the chip from the factory, the maker is destroying 18,835 finished devices and has halted shipping.
August 11, 2026 1:32 PM

How to Store a Seed Phrase Safely: What Steel, a Passphrase and Multisig Do for Your Wallet Backup
The Coldcard case pushed the manufacturer question to the front, while barely touching on where the backup is kept. This guide places paper, steel, the passphrase and splitting methods against the BIP-39 and SLIP-0039 standards.
June 25, 2024 11:00 PM
How to Buy Bitcoin on Bitget: A Step-by-Step Guide
Want to buy Bitcoin and still confused about which platform to use? Look no further! Check Bitget, and this full guide, step by step...
October 14, 2026 1:30 PM

What is a hardware wallet? How the device protects your keys
A hardware wallet stores no coins, only the private key, and it never releases it. How signing works inside the device, what the 12 or 24 words mean, and which attacks the design cannot stop.
September 23, 2026 4:12 AM

How to Set Up a Crypto Wallet: Securing Your Coins in Seven Steps
Your own crypto wallet is set up in twenty minutes, yet a single step decides everything that follows. This guide takes you through wallet type, recovery words and the test amount, and sets out what BaFin and the tax office expect.
October 2, 2026 10:36 AM
Hot Wallet or Cold Wallet: the Private Key Decides How Safe Your Coins Are
Hot wallet or cold wallet: the difference rests solely on whether the private key is online. What separates the two forms, where the limits of hardware lie and why moving to your own device triggers no tax.
September 30, 2026 7:16 AM

Tangem Wallet: The Card Without a Seed Phrase vs the Classic Hardware Wallet
The Tangem Wallet secures crypto with two or three identical cards instead of 24 words. What the sets cost, what the EAL6+ chip delivers and why losing every card is final.
October 10, 2026 10:35 PM
Fake Ledger Site Tops Google Search: “Once the recovery phrase has been handed over, the wallet must be regarded as compromised”
A security researcher reports a rebuilt Ledger site high up in Google's results that asks for the 24-word phrase. Running alongside it are emails with an invented deadline of October 15.
October 2, 2026 7:16 AM
$1.26 Billion in Three Months: Crypto Hacks Hit Their 2026 High
The security firm CertiK counts around $1.26 billion in damage from 247 incidents for the third quarter of 2026. September was the worst month of the year with 99 cases, and this is the background and what it means for your custody.
October 2, 2026 4:32 AM
NEAR Intents halts withdrawals after a $3.8 million exploit: here are the reasons
NEAR Intents confirms an exploit of more than $3.8 million and holds deposits and withdrawals on eleven networks. Reimbursement is promised, a date for it is not.
September 25, 2026 1:47 PM
Magic Eden and Limit Break exploit: 530 WETH and thousands of NFTs drained, how to revoke your approvals
A bug in Limit Break's Payment Processor, the protocol behind Magic Eden's former Ethereum marketplace, has been draining NFTs and WETH since Thursday. Our blockchain analysis shows 911 affected wallets. What happened, why hardware wallets do not protect you and which two approvals to revoke now.
September 3, 2026 10:21 AM
Bitcoin Lost in a Wallet Hack: What Tax Applies in Austria?
Bitcoin lost to hackers? In Austria, the theft of privately held coins generally does not create a capital loss you can use for tax. Only a later payout can change that.
October 26, 2026 12:26 AM
Keystone confirms data breach: “We owe you an apology”
Hardware wallet maker Keystone has disclosed a break-in at its web shop: customer names, delivery addresses and order details were taken. Recovery phrases and private keys are not affected, the company says, and the real risk lies with phishing and the home address now in the open.
September 25, 2026 4:11 AM

Bitget Pauses Withdrawals: Where Existing Customers in Europe Stand
Bitget reports unauthorised outflows of around $351.6 million (later revised to $387.5 million) and has suspended withdrawals. For existing customers in Europe, that closes the one route MiCA had left them.
September 20, 2026 4:15 PM
Crypto Phishing After a Data Breach: The Warning Signs in a Fake Exchange Email
After every major data breach, the number of phishing emails sent in the name of crypto exchanges and wallet manufacturers rises. This article shows you how to recognise such a message, which data a reputable provider never requests by email, and what to do in the first hour after a click.
September 7, 2026 7:26 PM
Stolen Keys Beat Code Flaws: Why the Private Key Is the Way In for 2026 Crypto Hacks
Compromised private keys overtook smart contract code flaws as the most common attack route for the first time in 2026. What sits behind the shift, and how to check your own setup for its single point of failure.
More from CryptoTicker